About us
Built so the next escalation never happens
37 Audits started on the receiving end of critical escalations: a site is down, a certificate expired, a search page is being hammered, a version has a known CVE. After each one the question was the same: how do we make sure this never happens again? The answer became a product.
Where it comes from
For nearly nineteen years the founder worked inside Liferay, from the core engineering team to leading the Solution Architects and Customer Experience Managers who keep the largest customers in Latin America running. That last role meant being the single point of contact when a critical site went down.
Most of those incidents were not exotic. They were an expired domain, a cache header that was never set, a fix release nobody applied, a control panel left open to the internet. Things a machine could have caught days earlier, if anyone had told it what to look for.
37 Audits is that machine. Each auditor encodes one lesson from production. Run it once, or let it watch your site and tell you the moment something changes.
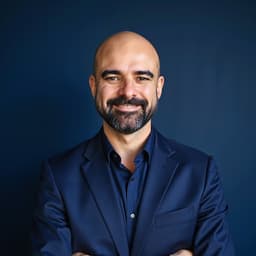
Thiago Moreira
Founder. Builds the auditors, answers the support inbox and runs 37 Audits from Florianópolis, Brazil.
How we work
Five rules every auditor and journey has to follow.
Check the thing that breaks
Every auditor comes from a real incident: an expired certificate, a search page that took a site down, a version with a known CVE. If it never hurt a production site, it is not an auditor.
Say why it matters
A red badge is useless without context. Each check explains what it found, why that is a risk and what a passing setup looks like, so the fix lands on the right desk.
Watch, do not just scan
A one-off report is stale the next deploy. Auditors can run as often as every three minutes and email the team the moment a check flips from pass to fail, or back.
Turn checklists into journeys
Go-live checklists live in PDFs nobody reopens. Journeys turn them into ordered steps, with auditors verifying what they can and manual steps for what only you can see.
Work with agents too
The same auditors are available through an API and an MCP server, so an AI agent can run, schedule and read audits the way a person does.
We audit ourselves
37audits.com is monitored by its own auditors, and the full per-check history is public. If a check fails on us, you can see it.
See Live Monitoring →
Talk to us
Missing an auditor for your stack, or want a journey for your platform? Tell us what broke last time.