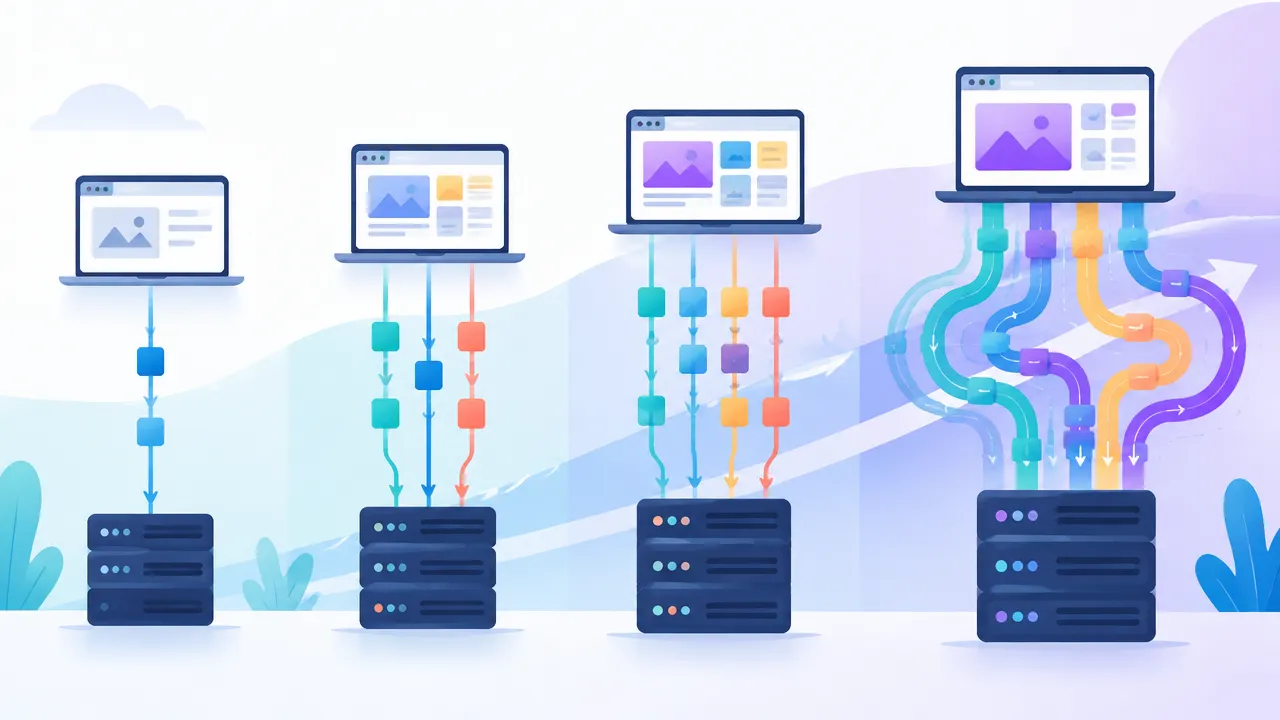
HTTP has four commonly referenced versions: HTTP/1.0, HTTP/1.1, HTTP/2, and HTTP/3. For most websites, I recommend enabling modern protocols while keeping a tested compatibility path for older clients.
Key takeaways for website owners
HTTP/3 is the newest standardized version, while HTTP/2 remains an important modern option.
HTTP/1.0 and HTTP/1.1 are earlier versions, while HTTP/2 and HTTP/3 are later major versions.
Retire HTTP/1.0 if your traffic and dependencies do not require it, but do not disable HTTP/1.1 without checking compatibility.
HTTP version does not replace HTTPS. Encryption and authentication depend on TLS configuration.
Test the protocol a real connection negotiates, not only what a server configuration claims to support.
Which HTTP versions are real?
HTTP/1.0 and HTTP/1.1 are the two established versions in the original text-based protocol family. HTTP/1.0 added headers and status codes to the early web protocol, while HTTP/1.1 introduced persistent connections and other improvements. The HTTP/1.0 specification documents the older version, and current HTTP/1.1 messaging rules are described in the HTTP/1.1 standard.
HTTP/2 and HTTP/3 are later major versions, not decimal extensions of HTTP/1. HTTP/2 changes how messages are framed and allows multiple streams over one connection. HTTP/3 carries HTTP semantics over QUIC. The relevant standards are the HTTP/2 specification and the HTTP/3 specification.
How do the versions differ in practice?
The practical differences are connection reuse, how data is framed, and the transport used. A newer version can improve efficiency, but the client and server must both support it and successfully negotiate it.
Version | What changed | Practical guidance |
|---|---|---|
HTTP/1.0 | Added headers, status codes, and support for more request methods and media types. | Keep only when a known legacy client needs it. |
HTTP/1.1 | Supports persistent connections and remains a widely useful fallback. | Retain for compatibility unless your measured requirements say otherwise. |
HTTP/2 | Uses binary framing and multiplexes streams over a connection. | Enable for modern clients and hosting environments that support it. |
HTTP/3 | Maps HTTP onto QUIC, which uses UDP as its transport. | Enable where available, and keep a fallback for clients that cannot use it. |
These differences do not guarantee that every page will load faster under a newer version. Results depend on the site, network conditions, server configuration, and the client. I use protocol support as one part of a performance review, then verify real page behavior and load times.
Should you turn off older HTTP versions?
I recommend removing HTTP/1.0 support when traffic data confirms that no required users or connected systems depend on it. Keeping a protocol enabled without a need can add legacy behavior to maintain and test. However, a blanket instruction to disable every older version is not a safe default.
HTTP/1.1 remains a useful fallback for clients and intermediaries that cannot negotiate HTTP/2 or HTTP/3. Disabling it can break access for some visitors, integrations, monitoring agents, or older software. Before changing settings, review access logs, supported-client requirements, and the configuration of any proxy or load balancer in front of the application.
For a careful retirement, I would:
Measure which versions real requests use over a representative period.
Identify business-critical clients and automated integrations.
Disable HTTP/1.0 in a test environment or for a limited rollout.
Watch for failed requests, support reports, and unexpected fallback behavior.
Keep HTTP/1.1 if it is still needed for broad compatibility.
Does the HTTP version determine whether a site is secure?
No. HTTP/2 or HTTP/3 does not, by itself, make a website secure, and HTTP/1.1 is not automatically a security risk. HTTPS uses TLS to protect traffic in transit. A site should use HTTPS consistently, redirect visitors from plaintext HTTP, and keep its TLS configuration current.
I review these as separate controls: the HTTP version affects message transport and efficiency, while HTTPS and TLS protect the connection. A newer protocol cannot compensate for an expired certificate, weak TLS settings, or pages that still load insecure resources. A TLS version audit can help identify configuration issues, while HTTP-to-HTTPS redirect checks can confirm that visitors are directed to the secure URL.
How should you roll out HTTP/2 and HTTP/3?
I recommend enabling modern versions alongside a compatible fallback, then measuring outcomes before changing the fallback policy. In many hosting setups, protocol negotiation happens at the edge or server connection rather than through a change to the website’s HTML. The exact setting depends on your host, proxy, and certificate configuration.
Use this rollout sequence:
Confirm your host or edge server supports HTTP/2 and HTTP/3.
Check that the site has valid HTTPS and that the certificate covers the hostname.
Enable HTTP/2 first if it is not already active, then test HTTP/3 where supported.
Verify that clients still connect when a newer protocol is unavailable.
Compare connection errors and performance measurements before and after rollout.
HTTP/3 is the latest standardized version, but “latest” does not mean it should be the only version offered. I prefer enabling it when practical while preserving the fallback that real visitors need.
How can you check which version your website uses?
Check the protocol negotiated by an actual browser or client connection, and repeat the check from more than one network or test environment. A configuration file may show what the server is intended to support, but the negotiated result can differ because of client capability, proxies, or network conditions.
37 Audits includes an HTTP version auditor to help identify the protocol a site supports. I would pair that check with review of HTTPS redirects and TLS settings, then recheck after server or hosting changes. Ongoing monitoring can reveal a regression that a one-time setup test might miss.
Frequently asked questions
Are HTTP/2 and HTTP/3 real protocol versions?
Yes. HTTP/2 and HTTP/3 are standardized HTTP versions. They are later major versions, not decimal extensions of HTTP/1. HTTP/2 and HTTP/3 are the second and third major versions, respectively.
Is HTTP/1.0 still used?
Yes, HTTP/1.0 can still appear in legacy clients, devices, or server configurations, but it is uncommon for modern browser traffic. I recommend checking actual connection logs before disabling it. If no required users depend on it, turning off HTTP/1.0 can simplify support for older behavior.
Should I use HTTP/1.1 or HTTP/2?
For most modern websites, I recommend enabling HTTP/2 and HTTP/3 where the hosting stack supports them, while retaining HTTP/1.1 as a compatibility fallback. HTTP/3 is the newest standardized version, but a client or network may not negotiate it, so offering only HTTP/3 can prevent some connections.
Is HTTP/1.1 a security risk?
No. HTTP/1.1 alone does not make a website insecure. Security depends on factors such as whether traffic uses HTTPS with correctly configured TLS, plus the server and application configuration. I recommend securing the connection first, then reviewing protocol support for compatibility, performance, and unnecessary legacy exposure.
Is HTTP/3 the latest HTTP version?
HTTP/3 is the newest standardized HTTP version among HTTP/1.0, HTTP/1.1, HTTP/2, and HTTP/3. It uses QUIC rather than TCP as its transport. I recommend enabling it when supported, while keeping appropriate fallbacks so clients that cannot negotiate HTTP/3 can still reach the site.